Cybercriminals and spies working for nation-states are surreptitiously coexisting inside the identical compromised name-brand routers as they use the units to disguise assaults motivated each by monetary acquire and strategic espionage, researchers mentioned.
In some instances, the coexistence is peaceable, as financially motivated hackers present spies with entry to already compromised routers in alternate for a price, researchers from safety agency Pattern Micro reported Wednesday. In different instances, hackers working in nation-state-backed superior persistent menace teams take management of units beforehand hacked by the cybercrime teams. Generally the units are independently compromised a number of instances by totally different teams. The result’s a free-for-all inside routers and, to a lesser extent, VPN units and digital non-public servers offered by internet hosting corporations.
“Cybercriminals and Superior Persistent Menace (APT) actors share a typical curiosity in proxy anonymization layers and Digital Personal Community (VPN) nodes to cover traces of their presence and make detection of malicious actions tougher,” Pattern Micro researchers Feike Hacquebord and Fernando Merces wrote. “This shared curiosity leads to malicious web site visitors mixing monetary and espionage motives.”
Pawn Storm, a spammer, and a proxy service
A superb instance is a community made up primarily of EdgeRouter units bought by producer Ubiquiti. After the FBI found it had been contaminated by a Kremlin-backed group and used as a botnet to camouflage ongoing assaults focusing on governments, militaries, and different organizations worldwide, it commenced an operation in January to quickly disinfect them.
The Russian hackers gained management after the units have been already contaminated with Moobot, which is botnet malware utilized by financially motivated menace actors not affiliated with the Russian authorities. These menace actors put in Moobot after first exploiting publicly recognized default administrator credentials that hadn’t been faraway from the units by the individuals who owned them. The Russian hackers—recognized by a wide range of names together with Pawn Storm, APT28, Forest Blizzard, Sofacy, and Sednit—then exploited a vulnerability within the Moobot malware and used it to put in customized scripts and malware that turned the botnet into a worldwide cyber espionage platform.
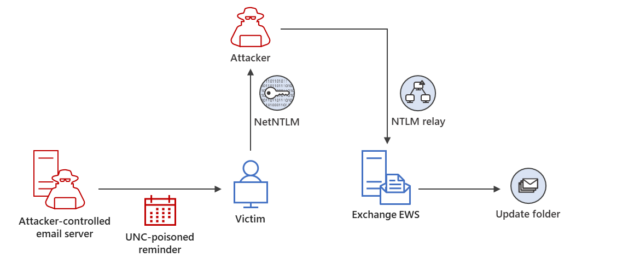
The Pattern Micro researchers mentioned that Pawn Storm was utilizing the hijacked botnet to proxy (1) logins that used stolen account credentials and (2) assaults that exploited a essential zero-day vulnerability in Microsoft Trade that went unfixed till March 2023. The zero-day exploits allowed Pawn Storm to acquire the cryptographic hash of customers’ Outlook passwords just by sending them a specifically formatted electronic mail. As soon as in possession of the hash, Pawn Storm carried out a so-called NTLMv2 hash relay assault that funneled logins to the consumer accounts by means of one of many botnet units. Microsoft offered a diagram of the assault pictured under:
Microsoft
Pattern Micro noticed the identical botnet getting used to ship spam with pharmaceutical themes which have the hallmarks of what’s referred to as the Canadian Pharmacy gang. Yet one more group put in malware referred to as Ngioweb on botnet units. Ngioweb was first present in 2019 working on routers from DLink, Netgear, and different producers, in addition to different units working Linux on high of x86, ARM, and MIPS {hardware}. The aim of Ngioweb is to offer proxies people can use to route their on-line actions by means of a collection of frequently altering IP addresses, significantly these situated within the US with reputations for trustworthiness. It’s not clear exactly who makes use of the Ngioweb-powered service.
The Pattern Micro researchers wrote:
Within the particular case of the compromised Ubiquiti EdgeRouters, we noticed {that a} botnet operator has been putting in backdoored SSH servers and a set of scripts on the compromised units for years with out a lot consideration from the safety business, permitting persistent entry. One other menace actor put in the Ngioweb malware that runs solely in reminiscence so as to add the bots to a commercially out there residential proxy botnet. Pawn Storm almost certainly simply brute compelled the credentials of the backdoored SSH servers and thus gained entry to a pool of EdgeRouter units they might abuse for varied functions.
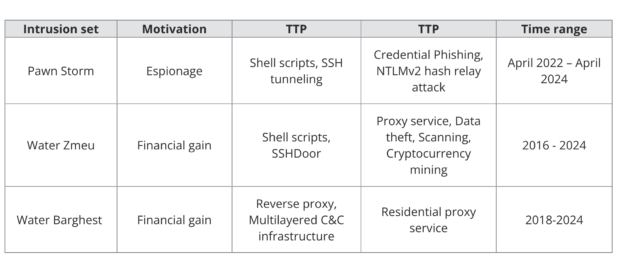
The researchers offered the next desk, summarizing the botnet-sharing association amongst Pawn Storm and the 2 different teams, tracked as Water Zmeu and Water Barghest:
Pattern Micro
It’s unclear if both of the teams was liable for putting in the beforehand talked about Moobot malware that the FBI reported discovering on the units. If not, that might imply routers have been independently contaminated by three financially motivated teams, along with Pawn Storm, additional underscoring the continued rush by a number of menace teams to ascertain secret listening posts inside routers. Pattern Micro researchers weren’t out there to make clear.
The submit went on to report that whereas the January operation by the FBI put a dent within the infrastructure Pawn Storm trusted, authorized constraints prevented the operation from stopping reinfection. What’s extra, the botnet additionally comprised digital public servers and Raspberry Pi units that weren’t affected by the FBI motion.
“Which means that regardless of the efforts of legislation enforcement, Pawn Storm nonetheless has entry to many different compromised property, together with EdgeServers,” the Pattern Micro report mentioned. “For instance, IP tackle 32[.]143[.]50[.]222 was used as an SMB reflector round February 8, 2024. The identical IP tackle was used as a proxy in a credential phishing assault on February 6 2024 in opposition to varied authorities officers all over the world.”